Everything a third-party risk program runs on
Five stages, one record, one audit trail. Each stage below is a working surface in the product, not a roadmap item.
Onboard
Vendor directory with tiering and dependencies, guided onboarding, an intake form you build from your own risk rubric, contracts with obligations mapped, and a renewal radar.
Assess
Campaign-driven questionnaires from a versioned template library and question bank. Suppliers answer in their own branded portal. Reviewers score against evidence.
Prioritise
A risk register with explainable composite scores, exposure lookup by entity or business unit, concentration analysis, and a monitoring inbox that turns external signals into work.
Remediate
Issues and remediation with owners and due dates, incident handling with severity and SLAs, and multi-step approval workflows that record who decided what.
Report
Analytics and reports on live data, scheduled board packs, saved views for the questions you ask every month, and a Trust Center you publish to your own customers.
Proof, not promises
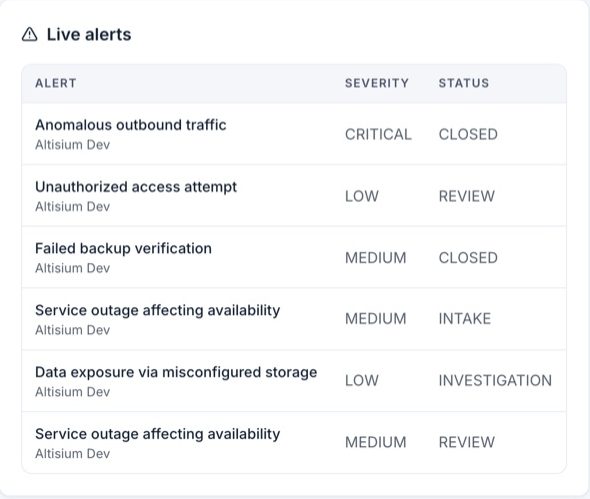
These are captures of the running application.



Open by design, honest about scope
We do not claim a marketplace of connectors we have not built. This is what is actually available today.
Security ratings
SecurityScorecard and BitSight adapters. Connect your own provider key and ratings land on the vendor record as a monitored signal, with movement tracked over time.
API and webhooks
Tenant-scoped API keys and webhook endpoints. Webhook payloads are signed with a timestamp bound into the signature, so a captured call cannot be replayed.
Single sign-on
SAML SSO with tenant-administered configuration, role-based access control, multi-factor authentication and a full activity log.
See the platform against your own suppliers.
We map Altisium onto the program you already run.